'/%3e%3cpath%20id='cross_2'%20data-name='cross%202'%20class='cls-2'%20d='M20.612,30.43h0a5.361,5.361,0,1,0-10.723,0H0A33.709,33.709,0,0,1,30.569,0V9.75a5.361,5.361,0,1,1,0,10.723V30.43Z'%20transform='translate(67.193%200.007)%20rotate(90)'/%3e%3cpath%20id='cross_3'%20data-name='cross%203'%20class='cls-3'%20d='M20.612,30.43h0a5.361,5.361,0,1,0-10.723,0H0A33.709,33.709,0,0,1,30.569,0V9.75a5.361,5.361,0,1,1,0,10.723V30.43Z'%20transform='translate(67.186%2067.041)%20rotate(180)'/%3e%3cpath%20id='cross_4'%20data-name='cross%204'%20class='cls-4'%20d='M20.6,30.5h0a5.361,5.361,0,1,0-10.723,0H0A33.71,33.71,0,0,1,30.56,0V9.818a5.361,5.361,0,1,1,0,10.723V30.5Z'%20transform='translate(0%2067.041)%20rotate(-90)'/%3e%3c/svg%3e)
API & site security
Manage the origins that may call WebSpace APIs and WebSocket from external browser apps, along with the CSP for deployed web pages.
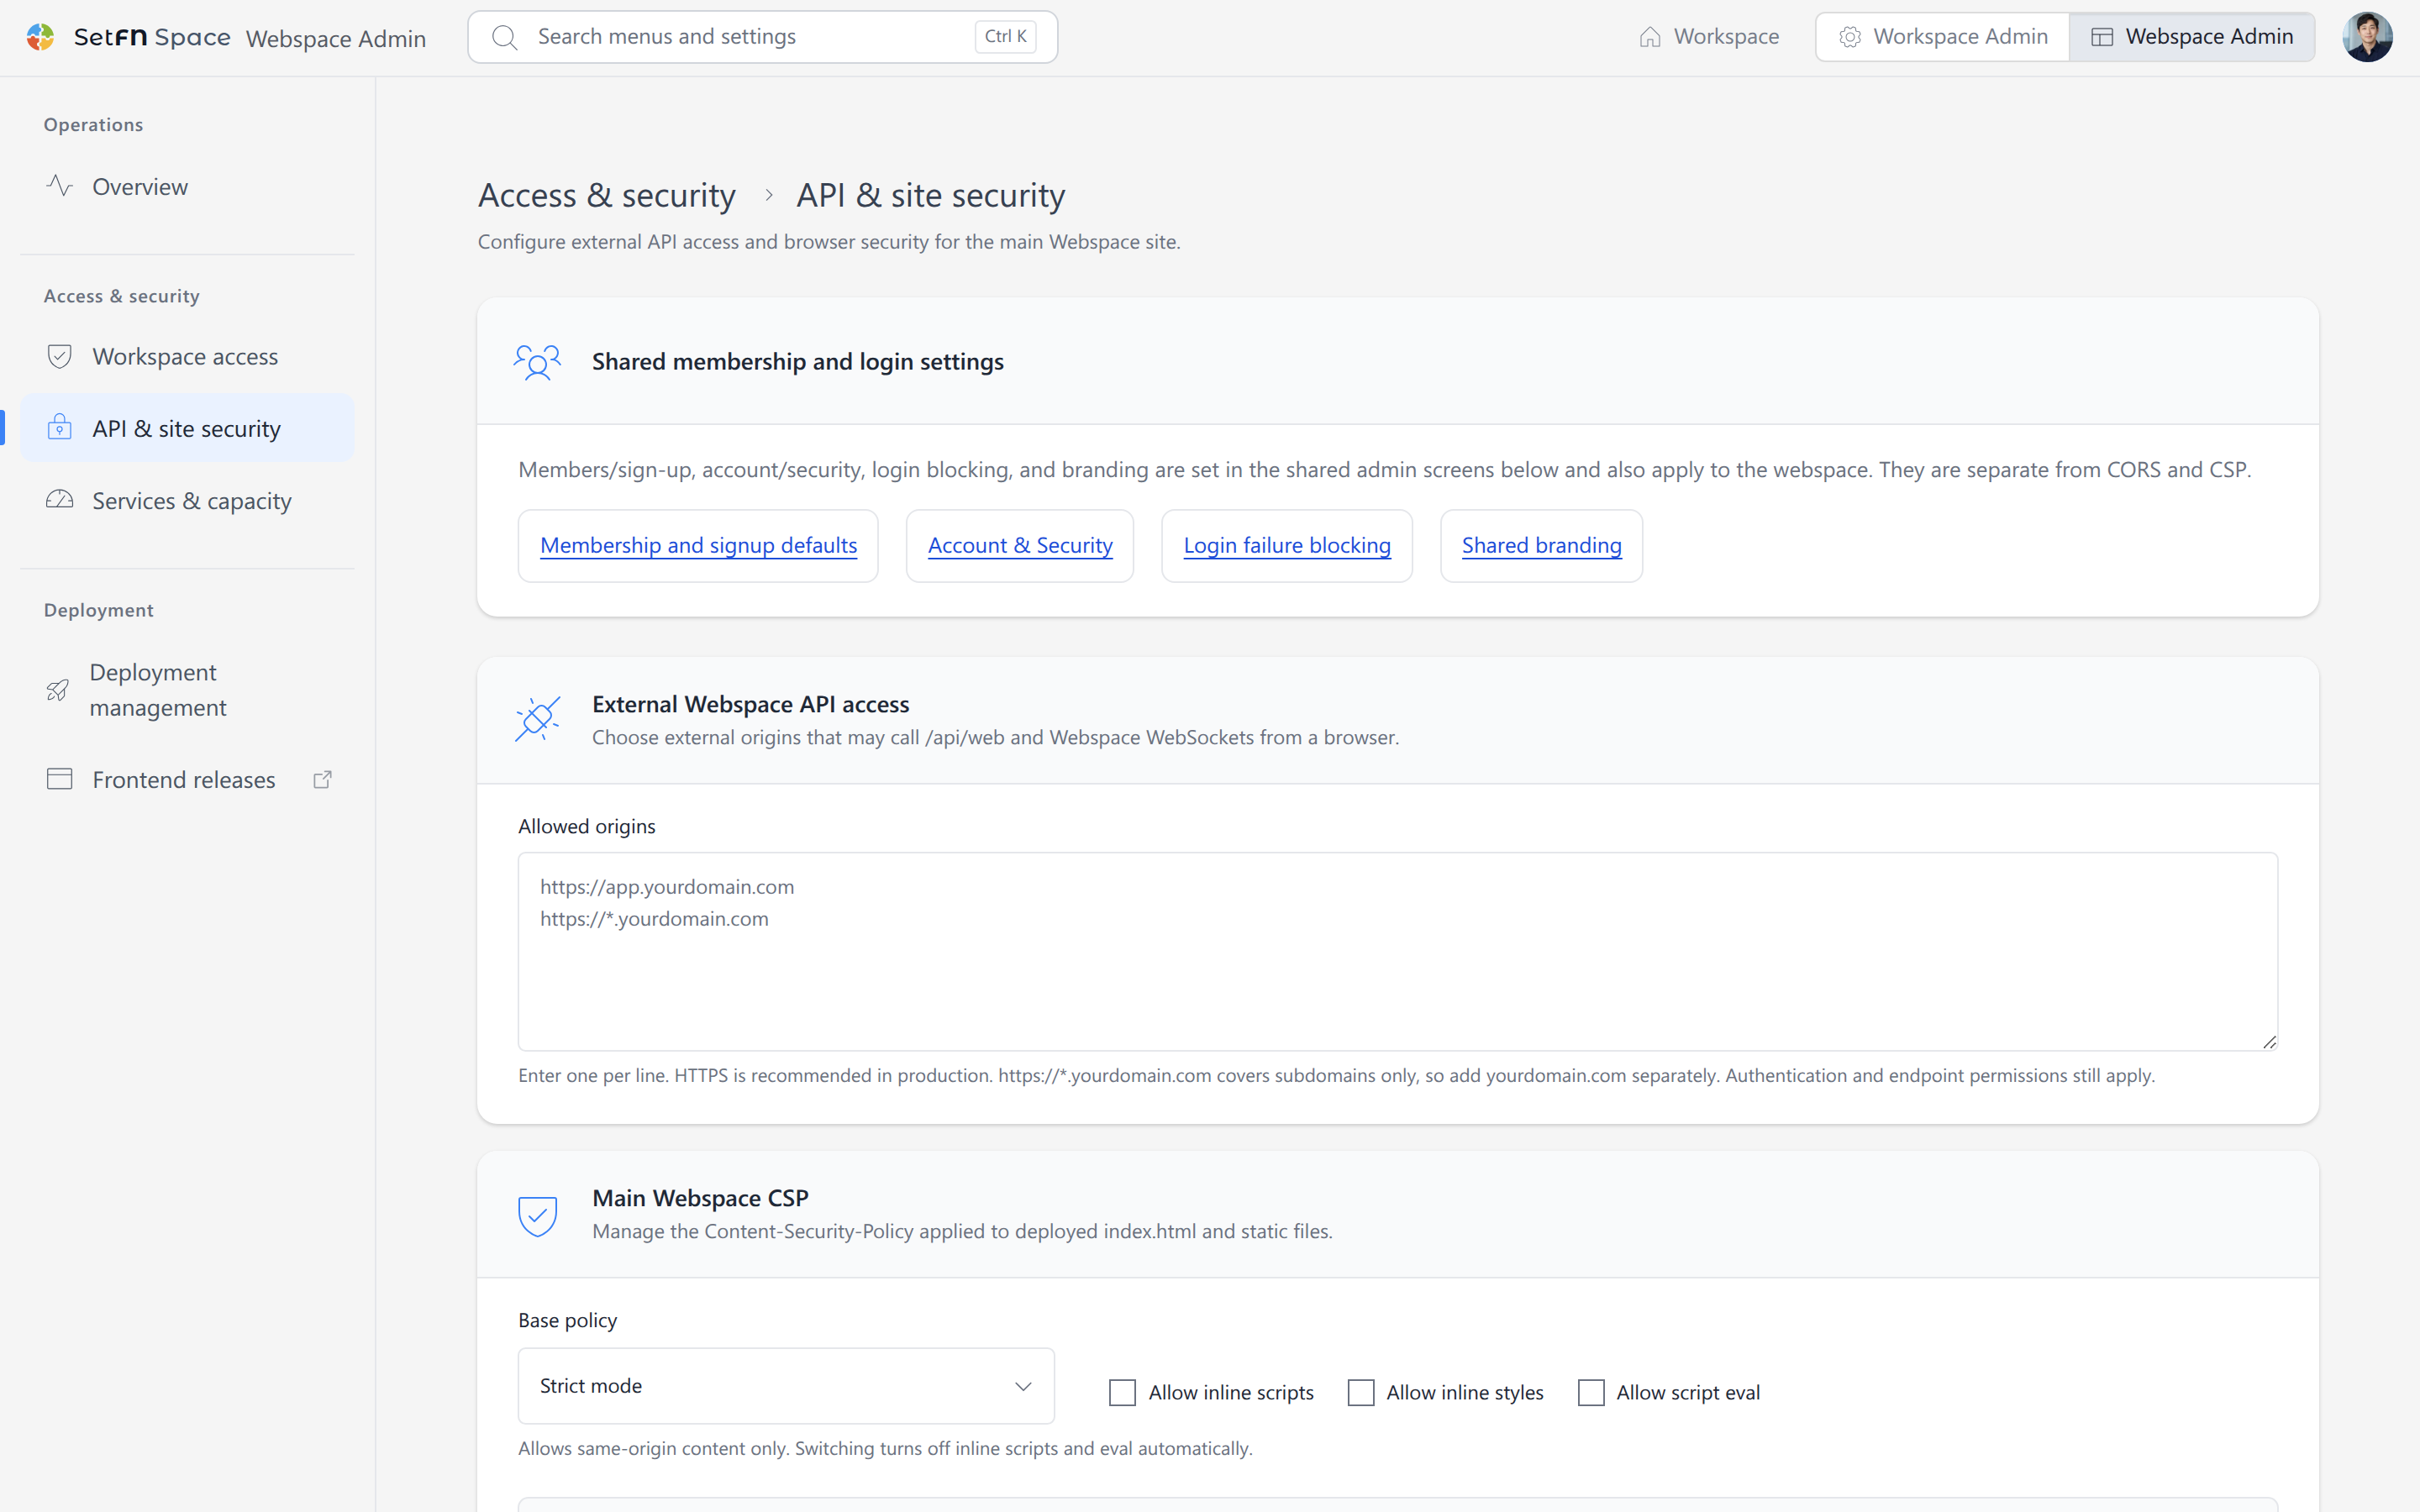
Allowed origins
Enter one origin per line.
https://app.example.com
https://*.example.com
A wildcard allows subdomains only. Registering https://*.example.com does not include https://example.com, so add it separately when needed. HTTPS is recommended for production services.
Origin permission defines the scope of cross-origin browser calls. Sign-in requirements and each SFN endpoint's ACL still apply.
Content-Security-Policy
- Web app compatibility: Use when you need broad support for external CDNs and common web app behavior.
- Strict mode: Restricts pages primarily to their own resources. Scripts and styles written directly inside the HTML and
evalare blocked, and a first frontend release starts in this mode. Check compatibility first for existing pages that need such code.
External domains lets you add sources separately for scripts, styles, images, fonts, connections, media, frames, and frame ancestors. Add only required domains. After saving, verify sign-in, APIs, WebSocket, images, and iframes at the deployed address.
The policy is written to frontend/security.json. An incorrect CSP can block a valid page, so record the current values before changing them.